Custom payment hardware can turn a straightforward embedded systems project into a demanding compliance program. A controller board may work perfectly on the bench, yet commercial deployment introduces security reviews, documented development practices, and ongoing maintenance obligations. Engineers must also account for encrypted payment data, physical tamper detection and certified software components. For many teams, the key decision is where custom engineering creates real value and where a commercially supported system can reduce cost and risk.
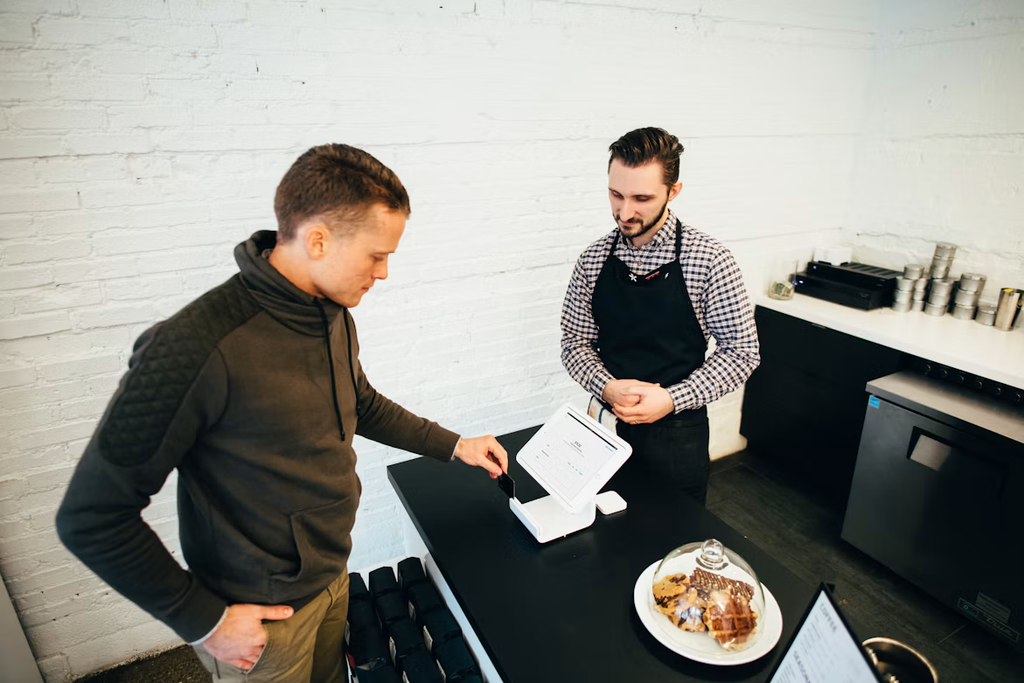
Photo by Blake Wisz on Unsplash
Table of Contents
The Real Cost of PCI Compliance
PCI compliance costs extend well beyond an initial assessment. Transaction volume and processing relationships affect the applicable validation requirements. A project may require vulnerability scans, penetration tests, policy documentation and employee training. Custom hardware also creates engineering expenses when firmware changes trigger security reviews or new test cycles.
The final bill depends on system complexity, cardholder data exposure and the amount of outside support required. These PCI cost factors show why teams should estimate compliance before finalizing architecture. Map every path that payment data follows, identify who maintains each component, and budget for recurring validation instead of treating certification as a one-time purchase.
Physical Anti-Tamper Mesh Engineering
A physical anti-tamper mesh uses closely spaced conductive traces to detect drilling, cutting or enclosure removal. The mesh can surround sensitive processors and memory, with monitoring circuits checking continuity or electrical characteristics. If the expected signal changes, the system may erase protected data, disable payment functions or record a security event.
Designing this protection takes more than adding traces to an unused PCB layer. Engineers must manage manufacturing tolerances, flex behavior, connector access and false alarms caused by temperature changes. Prototype the mesh early and test assembled units under vibration, heat and repeated enclosure stress. Document fault responses as carefully as the detection circuit because assessors need predictable behavior when tampering occurs.
Adopting an All-in-One POS Terminal
An integrated system can remove much of the payment-specific hardware burden from an embedded development team. A commercially supported POS terminal combines a large-format touchscreen, payment processing and a built-in receipt printer, with barcode scanning and mobile reader options available for business workflows.
Before adopting one, define clear boundaries between the terminal and your custom equipment. For example, a restaurant controller might send an order total through an approved integration while the terminal handles payment entry and receipts. Confirm interface support, offline behavior, update policies and data ownership before committing. This division lets engineers focus on application logic without expanding the custom board’s exposure to sensitive payment functions.
Where Custom Controller Boards Still Shine
Custom boards remain useful when a product needs specialized sensing, deterministic timing or direct control of equipment. A self-service kiosk may need to manage motors, status lights, environmental sensors and a local display while an external certified device handles transactions. Keeping these responsibilities separate simplifies fault diagnosis and allows either subsystem to change without redesigning the entire product.
Define the boundary at the schematic and software levels. Use a narrow command set, validate every incoming value and avoid storing payment details in logs or diagnostic memory. Include watchdog recovery, signed firmware updates and clearly labeled service connectors. The role of secure bootloaders in embedded systems also shows how firmware validation can prevent unauthorized code from running on deployed devices. The strongest design gives the custom controller a focused job, then proves through interface documentation that sensitive transaction data never enters it.
You can read the below tutorials.
Embedded Software | Firmware | Linux Devic Driver | RTOS
Hi, I am a tech blogger and an Embedded Engineer. I am always eager to learn and explore tech-related concepts. And also, I wanted to share my knowledge with everyone in a more straightforward way with easy practical examples. I strongly believe that learning by doing is more powerful than just learning by reading. I love to do experiments. If you want to help or support me on my journey, consider sharing my articles, or Buy me a Coffee! Thank you for reading my blog! Happy learning!
Share this:

Discover more from EmbeTronicX
Subscribe to get the latest posts sent to your email.